

Wireless Communication
 EU RED Network Security Standard EN 18031
 Wireless and communication detection
 Mobile communication product certification
 Bluetooth BQB Product Certification
 FM/AM Product Certification
 WiFi Product Certification
 Wireless charging product certification
 Interphone product certification
 Base station certification
 SAR testing
 Receiver Product Certification
 5G NR Product Certification
 UWB Product Certification
 Internet of Things authentication
Electromagnetic compatibility
 Automotive Electronics EMC Testing
 EMC rectification
 EMC
Automotive Electronics
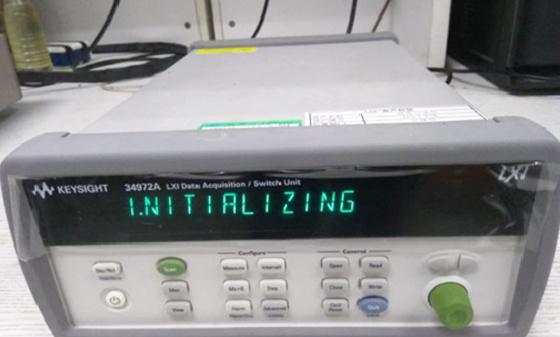 Electrical performance testing
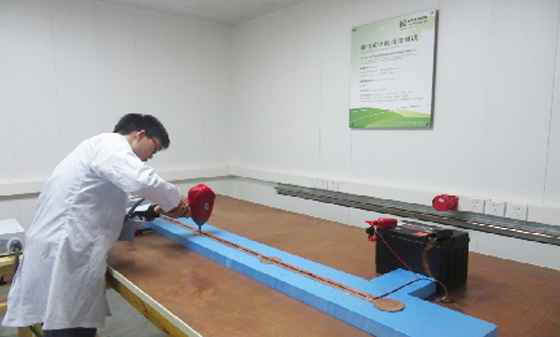 EMS testing - radiation anti-interference testing system (including radar waves)
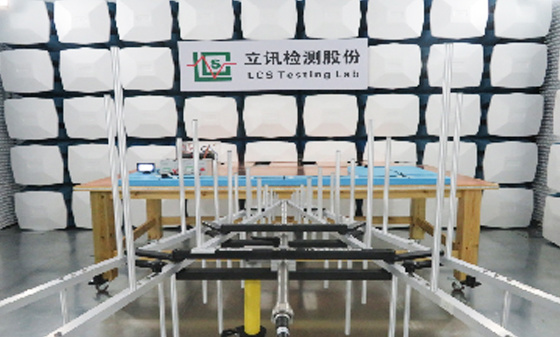 EMS Testing - Electrostatic Discharge
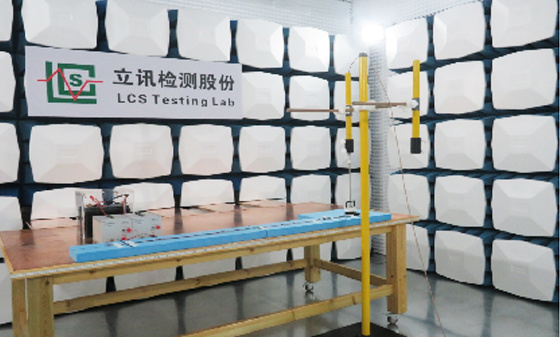 EMS Test - Transient Conducted Immunity Test
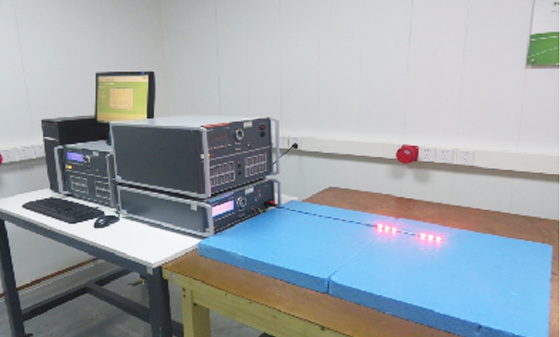 EMS Testing - Portable Transmitter Immunity
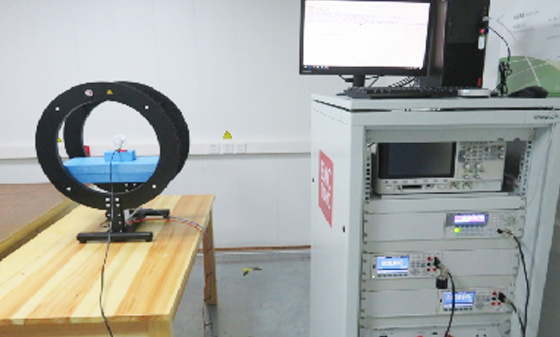 EMS Test - High Current Injection (BCI) Test
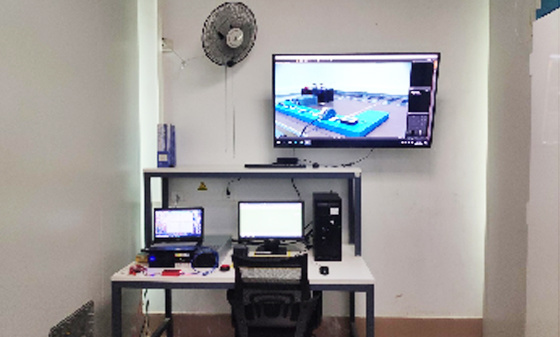 EMS test - low-frequency magnetic field anti-interference test
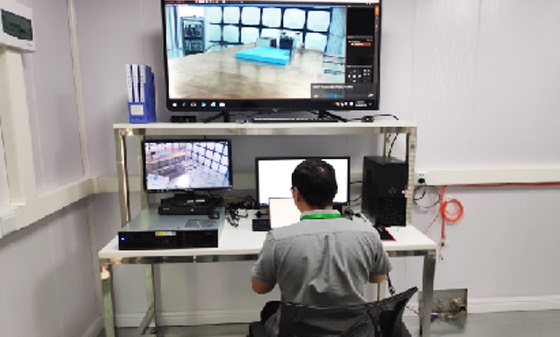 EMI Testing - Transient Conducted Emissions Testing System
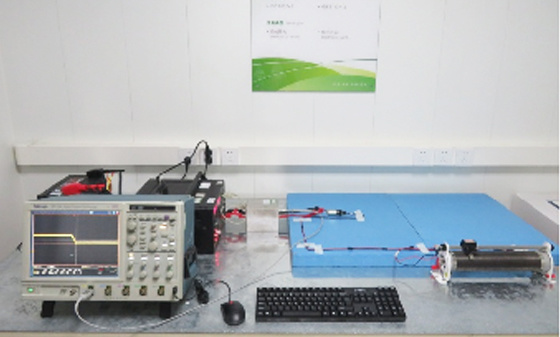 EMI testing - low-frequency magnetic field emission
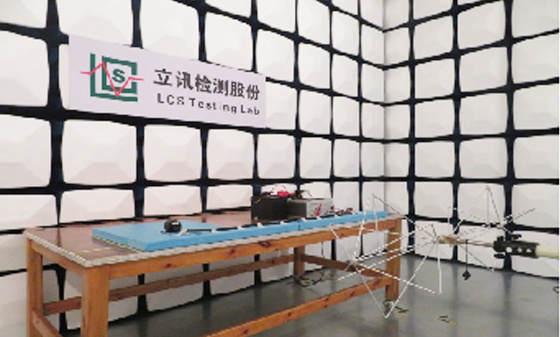 EMI Test - Radiation Emission Test
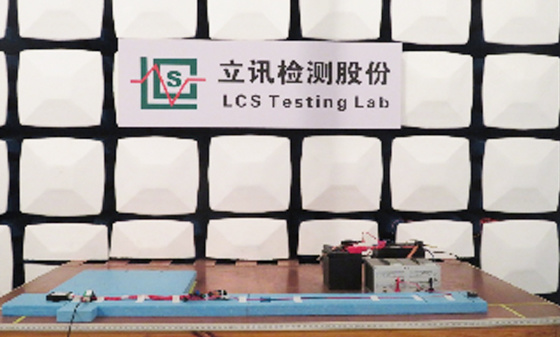 EMI Test - Conducted Emissions Test
 Automotive Electronic Testing
Automotive Parts Inspection
 Automotive ELV&VOC
 Reliability testing
 Temperature shock test
 Vibration testing
 Instrument panel/instrument panel three comprehensive vibration test
 Comprehensive vibration test of door inner panel III
 Sunvisor Three Comprehensive Vibration Test
 Spoiler Three Comprehensive Vibration Test
 Three comprehensive vibration tests of car front and rear bumpers
 Three comprehensive vibration tests for lamp housing/lampshade
 Comprehensive vibration test of outer circumference three
 Automotive metal material testing
 Performance testing of automotive lighting fixtures
 Rapid temperature change test
 Vibration
 Common issues with vibration testing
 Common issues with fatigue testing
 Common issues with high and low temperature testing
 Conducted Interference (CE) - Suzhou Lixun Standard
 Electromagnetic Radiation Tolerance Test (RS) - Suzhou LCS Standard
 Electrical Fast Pulse Withstand Test (EFT) - Suzhou LCS Standard
 Voltage flicker test - Suzhou LCS standard
Electronic appliances
 Household appliance product testing
 Electrical accessory product testing
 Household appliance testing
Chemical Testing
 Introduction to PFAS Testing
 MOSH/MOAH Mineral Oil Testing Service
 MOSH/MOAH Mineral Oil Testing and Certification Report Service
 Consumer Product Testing Services - WEEE Chapter
 Ecological textile testing
 Leather Footwear Inspection
 Food contact material testing
 Testing of toys and baby products
 Hazardous substance testing
Electronic Cigarette Testing
 Electronic cigarette detection
Reliability testing
 Other tests - pencil hardness test
 Mechanical testing - Packaging compression test
 Climate environment testing - Xenon lamp aging test
Battery Testing
 Power storage battery testing and certification
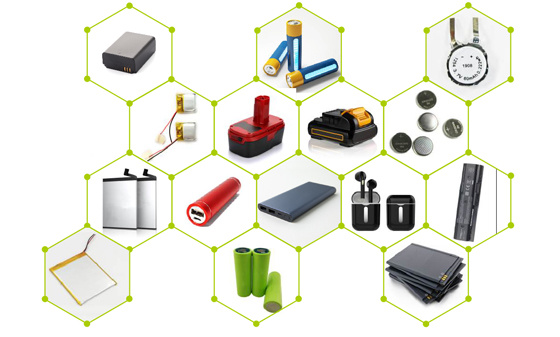 Consumer Electronics Battery Testing and Certification
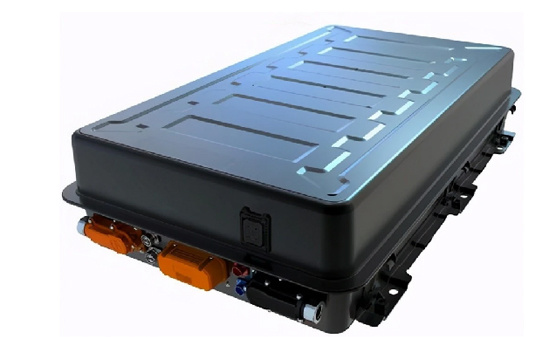 power battery
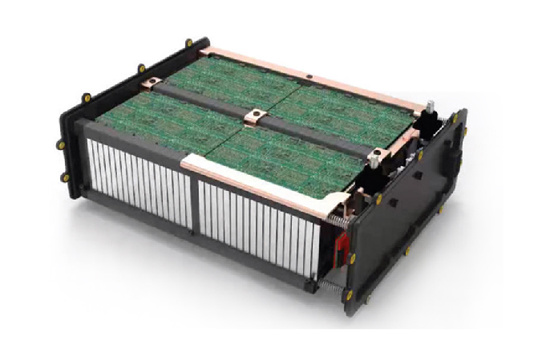 Light electric vehicle batteries
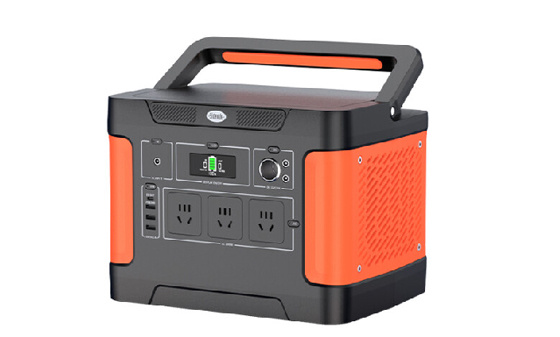 Energy storage battery
 Portable battery
 Battery testing
 battery test
Lamp Inspection
 Inspection of ship lighting fixtures
 COI Index Test for Medical Indoor Lighting
 Lamp safety inspection
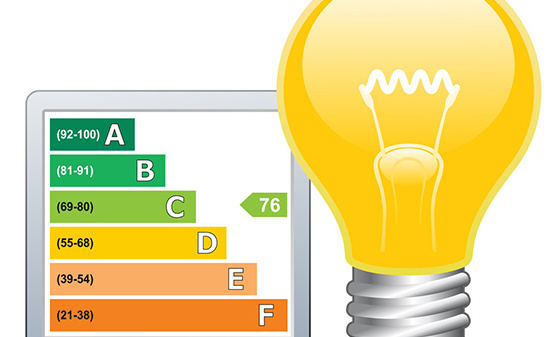 Luminaire energy efficiency testing
 EMC testing of lighting fixtures
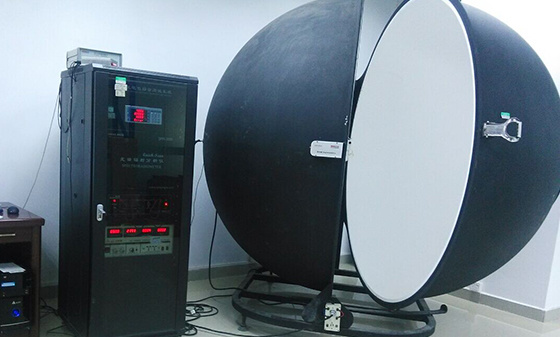 Integral Ball Laboratory
 Photobiology Experiment
 Light distribution test
 Lamp aging test
 Lamp IP waterproof
 Lamp performance testing
 Lamp reliability testing
Children's toy testing
 Testing standards for toy products
China Certification
 China's "national promotion" RoHS certification
 China Energy Efficiency Label Certification
 China Energy Conservation Certification
 China CQC Certification
 Tmall JD Quality Inspection Report
 China SRRC Certification
 Taiwan BSMI certification
 Taiwan NCC certification
 China CCC Compulsory Certification
Asia Certification
 Vietnam certification
 KC certification
 KUCAS Certification in Kuwait
 Singapore PSB certification
 Iraq COC Certification
 IMDA certification
 VCCI Certification in Japan
 JATE certification in Japan
 PSE certification
 BIS certification
 Japanese TELEC certification
European Certification
 RoHS certification
 GOST certification in Russia
 Russian EAC certification
 Northern Ireland UKNI logo
 Electrical ENEC certification
 European D-MARK certification
 Türkiye BTK certification
 TSE certification in Türkiye
 CE certification in Türkiye
 RED certification
 German TUV-SUD certification
 CE-ERP certification
 REACH certification
 German GS certification
 EU E-Mark certification
North American Certification
 Ecuador VOC certification
 Mexico NOM certification
 IRAM certification
 CPSC Certification in the United States
 CSA certification
 ASTM certification
 FDA certification
 CEC certification
 ETL certification
 ul certification
 IC certification
 Energy Star
 FCC Certification in the United States
 ASTM certification
Middle East Certification
 Israel SII certification
 Saudi SABER certification
 GCC certification for the seven Gulf countries
 Iran COI certification
 Qatar COC Certification
 Iraq COC Certification
 Saudi EER Energy Efficiency Certification
 Saudi SABER certification
 Algeria PCA certification
 PVOC certification
Australia Certification
 New Zealand IC-F testing
 VEET certification
 LCP certification
 GEMS certification
 RCM certification
 C-Tick certification
 SAA certification
Africa Certification
 Gabon COC certification
 Algeria COC certification

 Ethiopian VOC and COC certification
 Mauritius VOC certification
 Ghana COC certification
 COC certification in Burundi
 Zambia COC certification
 Botswana COC Certification
 Uganda PVOC certification
 SABS certification in South Africa
 South African LOA certification
 Zimbabwe CBCA Certification
 Nigeria SONCAP certification
 Kenya PVOC certification
 African COC certification
Other certifications
 WEEE
 Bluetooth BQB certification
 IECEE registration
 MHRA registration in the UK
TRAINING
 Management system training
 Laboratory technical training
 Laboratory Process Consulting
 Laboratory decoration construction
Wireless Communication
Electromagnetic compatibility
Automotive Electronics
Automotive Parts Inspection
Electronic appliances
Chemical Testing
Electronic Cigarette Testing
Reliability testing
Battery Testing
Lamp Inspection
Children's toy testing
China Certification
Asia Certification
European Certification
North American Certification
Middle East Certification
Australia Certification
Africa Certification
Other certifications
TRAINING

Heavy warning! Countdown to the CRA Act, can your product still smoothly export to the European Union?
Author.
LCS
Source:
Post time:
2026-07-13
Do you want to sell your product to Europe? You must know about this! The EU's Cyber Resilience Act (CRA) has officially come into effect. It is not a 'wolf', but a real one!
Starting from December 11, 2027, all software and hardware products with digital elements must comply with the strict requirements of the CRA in order to enter the EU market. Non compliant? The maximum fine is 15 million euros or 2.5% of global revenue! This is not a joke!
What exactly is CRA?
Simply put, it is the "cybersecurity rules" established by the European Union for all digital products.
It requires your product to firmly control network security throughout its entire lifecycle, from design to sales, use, and disposal.
Core: Introduce mandatory cybersecurity requirements for software and hardware products sold in the European Union.
Coverage: Security design, vulnerability handling, and ongoing maintenance throughout the product lifecycle.
Who is the "regulatory target" of CRA?
The coverage of CRA is beyond your imagination! As long as your product has "digital elements" and can be connected to the internet or process data, it is basically within range!
Ordinary contestants: printers, scanners, smart thermostats, various apps... Almost all the daily devices around you are listed!
Important Class I: Router VPN、 Antivirus software - the gatekeeper of network security.
Important Category II: Firewall, PKI (Public Key Infrastructure), Secure Encryption Hardware - Core Security Line of Defense.
Key products: smart meters, critical infrastructure operating systems - once a problem occurs, the consequences can be unimaginable!
CRA timeline
⚠️ Attention: The bill has come into effect, and the countdown to full compliance is less than 3 years!
👉 December 10, 2024: The CRA Act has officially come into effect!
👉 September 11, 2026: If any vulnerabilities or serious incidents that have been actively exploited are discovered in the product, mandatory reporting is required!
👉 December 11, 2027: Products placed on the EU market must fully comply with all CRA requirements!
What exactly does CRA need to test?
CRA is not just about running a few tests, it requires you to establish a complete and systematic network security management system.
Process compliance: It's not just about the results, but also about whether your R&D process is "safe". For example, does your development team have a rigorous security development management system? (Benchmarking against general network resilience principles such as prEN40000-1-2)
Technical verification: Based on the product type, select the corresponding international standards for technical verification to ensure the "hard power" of the product itself! For example, industrial products are benchmarked against 62443-4-2, while consumer IoT products are benchmarked against 303645. (LCS helps you choose the right standards)
Implementation system: Establish a complete "security development lifecycle" and prepare a series of supporting materials:
SBOM (Software Bill of Materials)
Mandatory Risk Analysis Report
Vulnerability Scanning Report
Penetration testing report
Patch update plan, etc
Ultimately, it may be necessary for authoritative institutions to issue a declaration of conformity or certification!
The ability to handle vulnerabilities is of utmost importance!
CRA has very strict and immediate requirements for vulnerability handling:
Discovering vulnerabilities being actively exploited? Must report to CSIRT/ENISA within 24 hours!
Zero day vulnerability? If active malicious exploitation is confirmed, it must be reported immediately!
Patch quickly! Security patches must be released in a timely manner and separated from feature updates to ensure that users can prioritize applying security patches.
The cost of non-compliance
As mentioned earlier, failure to comply with CRA will result in a hefty fine of up to 15 million euros or 2.5% of the company's global annual revenue (whichever is higher)!
More importantly, the product will be banned from being sold in the EU market, losing a huge market! This is a fatal blow to any company aspiring to go global.
CRA has come into effect, compliance is urgent!
Opportunities and challenges coexist in the EU market. The arrival of the CRA bill has put forward higher requirements for product network security, but it also means that only companies that truly value security can stand out in the competition.
Is your company ready? Don't wait until the last moment to get flustered! Take immediate action, assess product risks, establish a compliance system, and ensure your product operates smoothly in the EU market!
👉 If you have any CRA compliance questions, please feel free to private message us anytime for professional consulting services! Let us help you seize the opportunity and go out to sea without worry!
Related articles
New articles
Interpretation of LITE technology 9th issue
2026-09-28
Interpretation of LITE Technology 8th Issue
2026-09-24
Media Center
Latest News
Contact Us
National 24-hour service hotline
400-116-2629
Group Headquarters
E-mail: webmaster@lcs-cert.com
Address: Shenzhen City, Baoan District, Shajing Street, Nga side of the school of Wei Juji Industrial Park, Building A 1 ~ 2 floor, Building C 3 floor


 WeChat Inquiry


 Reservation


Contact Us
National 24-hour service hotline
Address:Juji Industrial Park, Xueziwei, Ngabian, Shajing Street, Baoan District, Shenzhen Building A 1~2F, Building C 3F

WeChat public number
Share industry dry goods

WeChat consultation
Please note consulting services

Follow Jitterbug

Mobile website
di complaint mailbox: customer.complaint@lcs-cert.com complaint telephone tel: 18126445450 certificate report verification of authenticity mailbox: verification@lcs-cert.com