

Wireless Communication
 EU RED Network Security Standard EN 18031
 Wireless and communication detection
 Mobile communication product certification
 Bluetooth BQB Product Certification
 FM/AM Product Certification
 WiFi Product Certification
 Wireless charging product certification
 Interphone product certification
 Base station certification
 SAR testing
 Receiver Product Certification
 5G NR Product Certification
 UWB Product Certification
 Internet of Things authentication
Electromagnetic compatibility
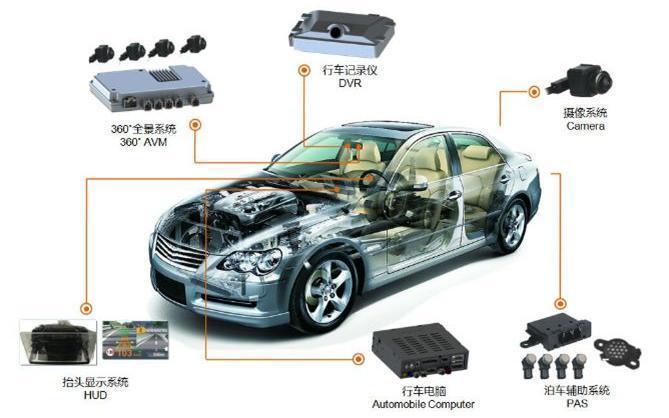 Automotive Electronics EMC Testing
 EMC rectification
 EMC
Automotive Electronics
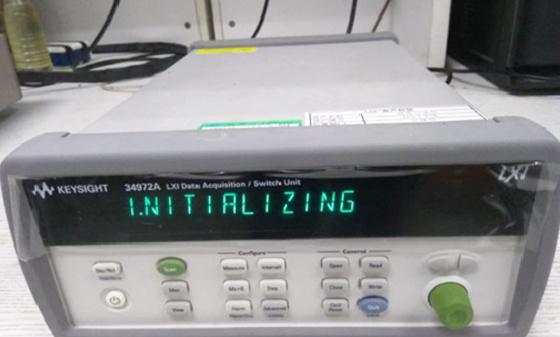 Electrical performance testing
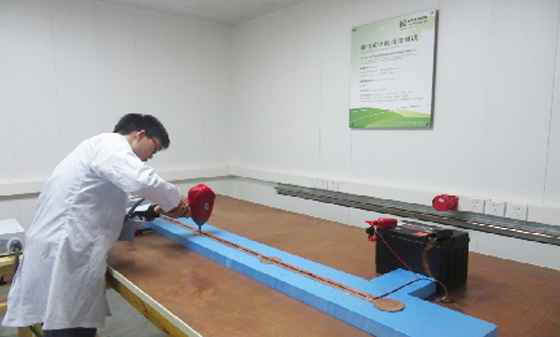 EMS testing - radiation anti-interference testing system (including radar waves)
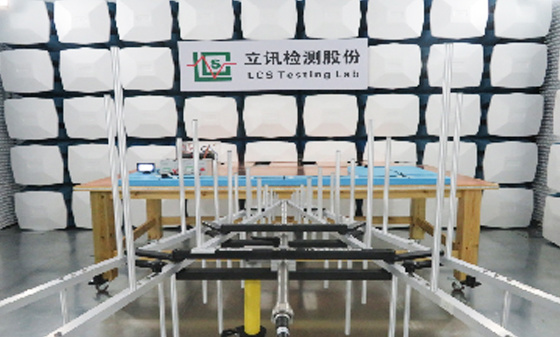 EMS Testing - Electrostatic Discharge
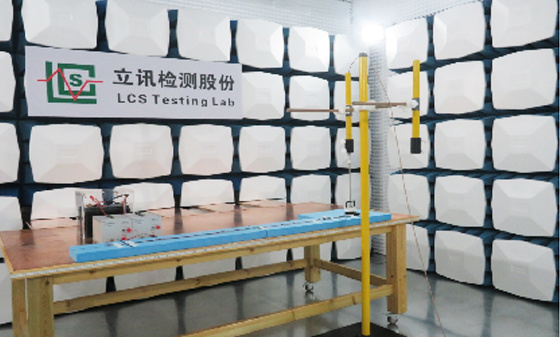 EMS Test - Transient Conducted Immunity Test
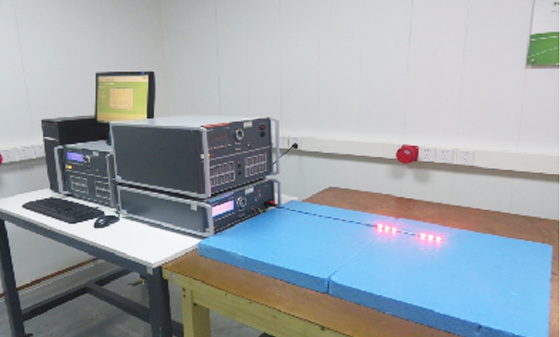 EMS Testing - Portable Transmitter Immunity
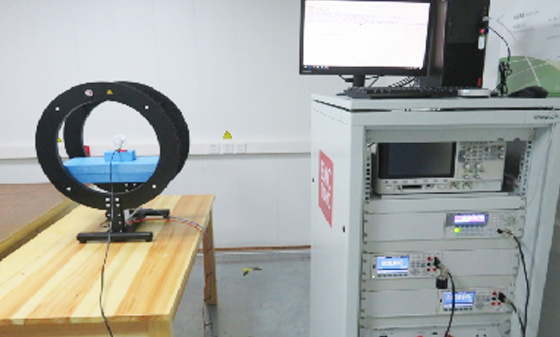 EMS Test - High Current Injection (BCI) Test
 EMS test - low-frequency magnetic field anti-interference test
 EMI Testing - Transient Conducted Emissions Testing System
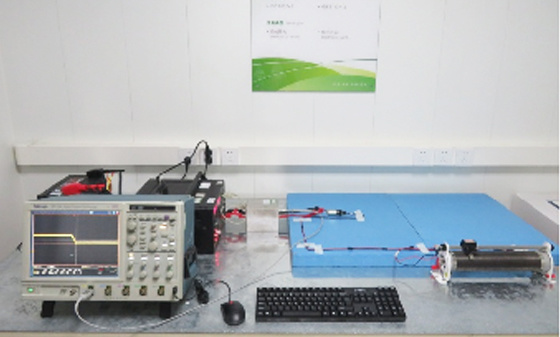 EMI testing - low-frequency magnetic field emission
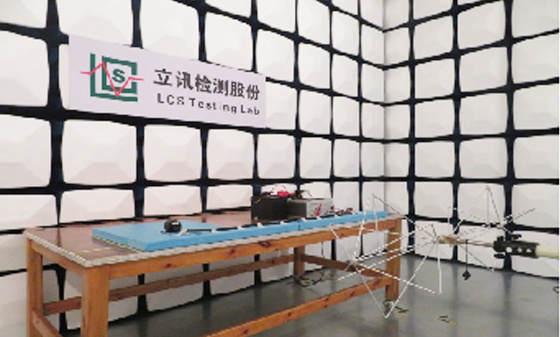 EMI Test - Radiation Emission Test
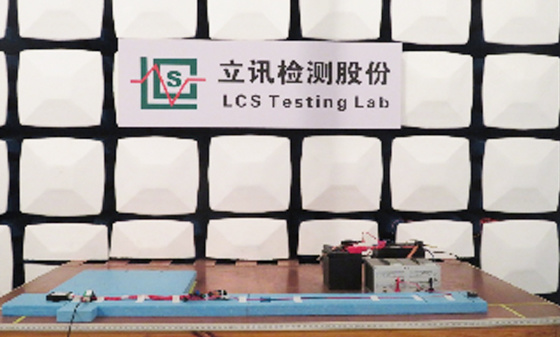 EMI Test - Conducted Emissions Test
 Automotive Electronic Testing
Automotive Parts Inspection
 Automotive ELV&VOC
 Reliability testing
 Temperature shock test
 Vibration testing
 Instrument panel/instrument panel three comprehensive vibration test
 Comprehensive vibration test of door inner panel III
 Sunvisor Three Comprehensive Vibration Test
 Spoiler Three Comprehensive Vibration Test
 Three comprehensive vibration tests of car front and rear bumpers
 Three comprehensive vibration tests for lamp housing/lampshade
 Comprehensive vibration test of outer circumference three
 Automotive metal material testing
 Performance testing of automotive lighting fixtures
 Rapid temperature change test
 Vibration
 Common issues with vibration testing
 Common issues with fatigue testing
 Common issues with high and low temperature testing
 Conducted Interference (CE) - Suzhou Lixun Standard
 Electromagnetic Radiation Tolerance Test (RS) - Suzhou LCS Standard
 Electrical Fast Pulse Withstand Test (EFT) - Suzhou LCS Standard
 Voltage flicker test - Suzhou LCS standard
Electronic appliances
 Household appliance product testing
 Electrical accessory product testing
 Household appliance testing
Chemical Testing
 Introduction to PFAS Testing
 MOSH/MOAH Mineral Oil Testing Service
 MOSH/MOAH Mineral Oil Testing and Certification Report Service
 Consumer Product Testing Services - WEEE Chapter
 Ecological textile testing
 Leather Footwear Inspection
 Food contact material testing
 Testing of toys and baby products
 Hazardous substance testing
Electronic Cigarette Testing
 Electronic cigarette detection
Reliability testing
 Other tests - pencil hardness test
 Mechanical testing - Packaging compression test
 Climate environment testing - Xenon lamp aging test
Battery Testing
 Power storage battery testing and certification
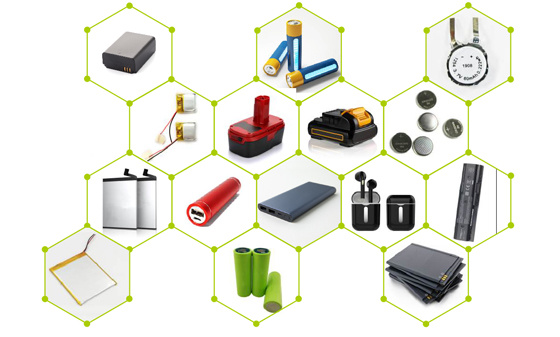 Consumer Electronics Battery Testing and Certification
 power battery
 Light electric vehicle batteries
 Energy storage battery
 Portable battery
 Battery testing
 battery test
Lamp Inspection
 Inspection of ship lighting fixtures
 COI Index Test for Medical Indoor Lighting
 Lamp safety inspection
 Luminaire energy efficiency testing
 EMC testing of lighting fixtures
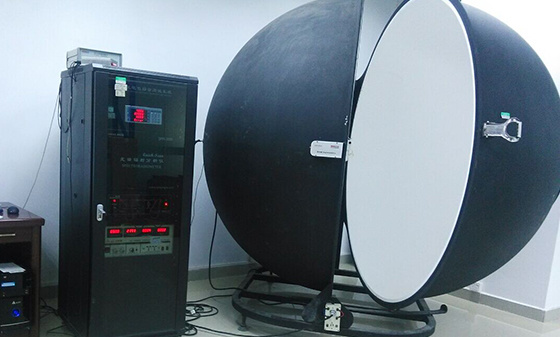 Integral Ball Laboratory
 Photobiology Experiment
 Light distribution test
 Lamp aging test
 Lamp IP waterproof
 Lamp performance testing
 Lamp reliability testing
Children's toy testing
 Testing standards for toy products
China Certification
 China's "national promotion" RoHS certification
 China Energy Efficiency Label Certification
 China Energy Conservation Certification
 China CQC Certification
 Tmall JD Quality Inspection Report
 China SRRC Certification
 Taiwan BSMI certification
 Taiwan NCC certification
 China CCC Compulsory Certification
Asia Certification
 Vietnam certification
 KC certification
 KUCAS Certification in Kuwait
 Singapore PSB certification
 Iraq COC Certification
 IMDA certification
 VCCI Certification in Japan
 JATE certification in Japan
 PSE certification
 BIS certification
 Japanese TELEC certification
European Certification
 RoHS certification
 GOST certification in Russia
 Russian EAC certification
 Northern Ireland UKNI logo
 Electrical ENEC certification
 European D-MARK certification
 Türkiye BTK certification
 TSE certification in Türkiye
 CE certification in Türkiye
 RED certification
 German TUV-SUD certification
 CE-ERP certification
 REACH certification
 German GS certification
 EU E-Mark certification
North American Certification
 Ecuador VOC certification
 Mexico NOM certification
 IRAM certification
 CPSC Certification in the United States
 CSA certification
 ASTM certification
 FDA certification
 CEC certification
 ETL certification
 ul certification
 IC certification
 Energy Star
 FCC Certification in the United States
 ASTM certification
Middle East Certification
 Israel SII certification
 Saudi SABER certification
 GCC certification for the seven Gulf countries
 Iran COI certification
 Qatar COC Certification
 Iraq COC Certification
 Saudi EER Energy Efficiency Certification
 Saudi SABER certification
 Algeria PCA certification
 PVOC certification
Australia Certification
 New Zealand IC-F testing
 VEET certification
 LCP certification
 GEMS certification
 RCM certification
 C-Tick certification
 SAA certification
Africa Certification
 Gabon COC certification
 Algeria COC certification

 Ethiopian VOC and COC certification
 Mauritius VOC certification
 Ghana COC certification
 COC certification in Burundi
 Zambia COC certification
 Botswana COC Certification
 Uganda PVOC certification
 SABS certification in South Africa
 South African LOA certification
 Zimbabwe CBCA Certification
 Nigeria SONCAP certification
 Kenya PVOC certification
 African COC certification
Other certifications
 WEEE
 Bluetooth BQB certification
 IECEE registration
 MHRA registration in the UK
TRAINING
 Management system training
 Laboratory technical training
 Laboratory Process Consulting
 Laboratory decoration construction
Wireless Communication
Electromagnetic compatibility
Automotive Electronics
Automotive Parts Inspection
Electronic appliances
Chemical Testing
Electronic Cigarette Testing
Reliability testing
Battery Testing
Lamp Inspection
Children's toy testing
China Certification
Asia Certification
European Certification
North American Certification
Middle East Certification
Australia Certification
Africa Certification
Other certifications
TRAINING

be careful! The EN 18031 series standards have officially become the coordination standards of the RED directive
Author.
LCS
Source:
Post time:
2025-03-24

On January 30, 2025, the European Commission officially included the EN 18031 series of standards in the list of coordinated standards for the Radio Equipment Directive (RED) in the Official Journal of the European Union (OJ), marking that this series of standards has become an important basis for network security compliance of radio equipment within the EU. The new regulations will be enforced from August 1, 2025, undoubtedly posing an urgent requirement for manufacturers to take immediate action.
New regulations content
RED directive strengthens network security requirements
According to the European Union's Radio Equipment Directive (RED), all radio equipment sold in Europe must meet mandatory requirements such as network security and privacy protection. The newly added Article 3 (3) in 2022 specifies three core requirements:
Preventing network attacks and service interruptions (clause d)
Personal Data and Privacy Protection (Clause e)
Preventing virtual currency fraud (clause f)
Interpretation of New Regulations
The three major restrictive clauses of EN 18031 series
The EN 18031 series standards provide specific technical specifications for the above requirements. With the inclusion of the EN 18031 series in the OJ, companies are allowed to use self declaration or third-party conformity assessment methods to meet compliance requirements. But manufacturers need to pay special attention to their official restriction clauses, otherwise they may not be able to pass the compliance declaration:
Limitation 1: The "Background" and "Guidelines" sections in the standard are invalid
The "rational" and "guidance" sections in EN 18031-1/2/3 are for reference only and do not serve as a basis for compliance.
Restriction 2: Allow users to not set a password (including PIN code)
If the device uses authenticated passwords for user authentication and allows users to use the product without setting or using any passwords (including PIN codes), it cannot be declared compliant in the form of a self-assessment statement.
For example, if mobile phones and tablets allow "password free use", a third-party qualification assessment path must be used.
However, please note that if the device pairing uses a key for identity authentication instead of a password, it can be compliant in the form of a self-assessment statement.
Limitation Three: Additional Requirements for Special Scenarios
A. For children's toys and monitoring equipment (applicable to EN 18031-2):
If the device adopts role-based, autonomous, or mandatory access control, but does not support parental/guardian control management permissions, a self-assessment statement cannot be used to claim compliance, and a third-party qualification assessment method must be used.
For example, the products involved include children's toys, wearable devices, and wireless devices for infant monitoring.
However, due to the relatively high risks associated with children's toys and monitoring equipment, it is highly recommended that companies adopt a third-party qualification assessment pathway.
B. Financial functional equipment (applicable to EN 18031-3):
The products involved include wireless devices that support virtual currency transactions (such as payment terminals, cryptocurrency hardware wallets). If only meeting the "security update" clause in the standard (such as digital signatures, secure communication, and other single measures) is not enough to prevent financial risks, multiple protection mechanisms need to be combined. Third party qualification assessment method must be adopted.
In summary, if a company falls under the three restrictions mentioned above, it cannot adopt a self-assessment statement and must use a third-party qualification assessment method to ensure compliance.
Compliance Path
Manufacturers must follow four steps
Given that the new regulations will be enforced from August 1, 2025, manufacturers must initiate the following work as soon as possible:
1. Confirm the scope of application of the product
Determine whether the equipment categories classified according to EN 18031-1/2/3 are subject to the new regulations.
2. In depth interpretation of EN 18031 standard clauses
Fully understand the applicable terms and limitations of the standard.
3. Compliance gap analysis
Compare the standard requirements and evaluate whether the existing design meets the restriction clauses, especially checking the password mandatory setting, parental control and other functions.
4. Self declaration or third-party agency intervention evaluation
Collaborating with third-party organizations is not only a compliance requirement (if using alternative solutions outside of standards), but also a key factor in ensuring compliance.
The EN 18031 series standards provide a clear path for RED compliance, simplifying the compliance process, but their restrictive clauses also emphasize market access requirements. It is clear that if the device is subject to restrictive clauses, the participation of a third-party organization (notified body) is still required to issue an EU Type Examination certification certificate.
The urgent task is for manufacturers to prioritize the investigation of high-risk areas such as password strategies, child device permissions, and financial function protection. At the same time, they should collaborate with third-party organizations to conduct assessments to avoid delays in product market access due to misinterpretation of standards.
Related articles
New articles
Media Center
Latest News
Contact Us
National 24-hour service hotline
400-116-2629
Group Headquarters
E-mail: webmaster@lcs-cert.com
Address: Shenzhen City, Baoan District, Shajing Street, Nga side of the school of Wei Juji Industrial Park, Building A 1 ~ 2 floor, Building C 3 floor


 WeChat Inquiry


 Reservation


Contact Us
National 24-hour service hotline
Address:Juji Industrial Park, Xueziwei, Ngabian, Shajing Street, Baoan District, Shenzhen Building A 1~2F, Building C 3F

WeChat public number
Share industry dry goods

WeChat consultation
Please note consulting services

Follow Jitterbug

Mobile website
di complaint mailbox: customer.complaint@lcs-cert.com complaint telephone tel: 18126445450 certificate report verification of authenticity mailbox: verification@lcs-cert.com