

Wireless Communication
 EU RED Network Security Standard EN 18031
 Wireless and communication detection
 Mobile communication product certification
 Bluetooth BQB Product Certification
 FM/AM Product Certification
 WiFi Product Certification
 Wireless charging product certification
 Interphone product certification
 Base station certification
 SAR testing
 Receiver Product Certification
 5G NR Product Certification
 UWB Product Certification
 Internet of Things authentication
Electromagnetic compatibility
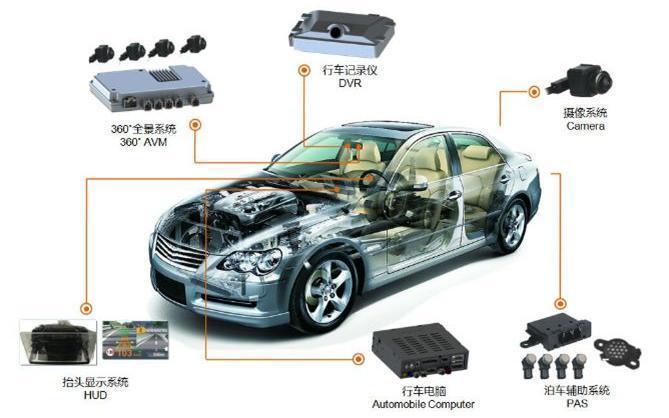 Automotive Electronics EMC Testing
 EMC rectification
 EMC
Automotive Electronics
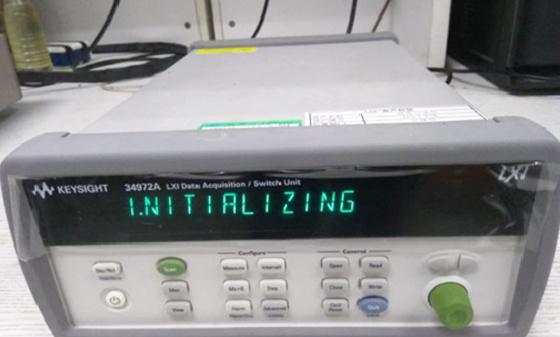 Electrical performance testing
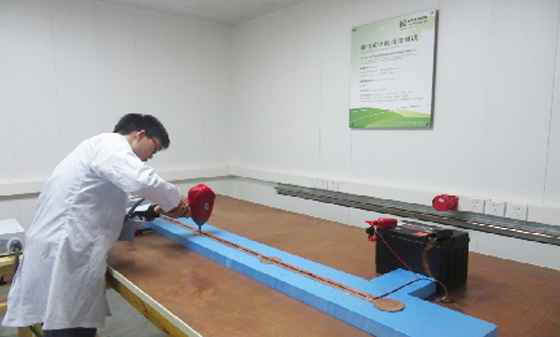 EMS testing - radiation anti-interference testing system (including radar waves)
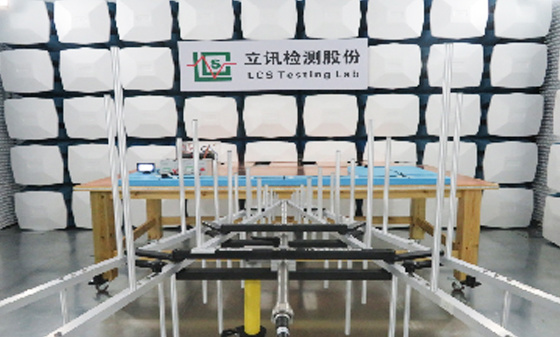 EMS Testing - Electrostatic Discharge
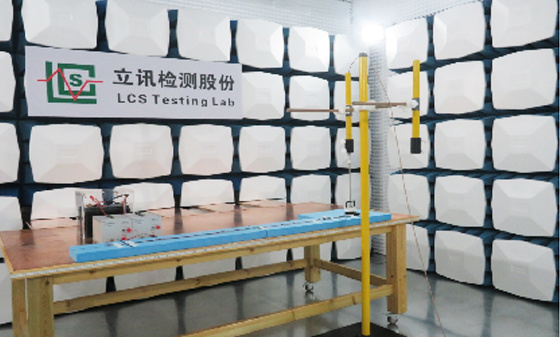 EMS Test - Transient Conducted Immunity Test
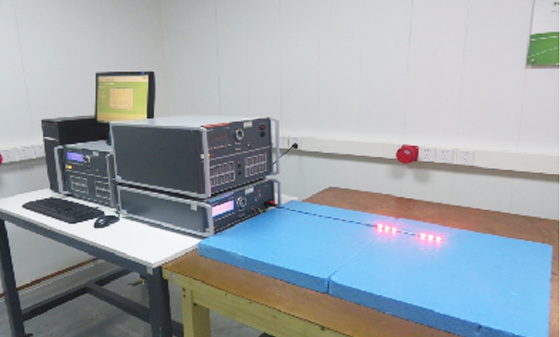 EMS Testing - Portable Transmitter Immunity
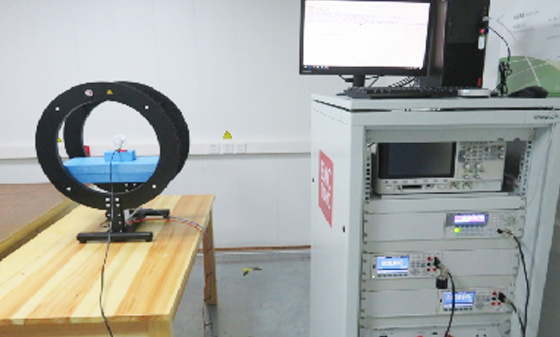 EMS Test - High Current Injection (BCI) Test
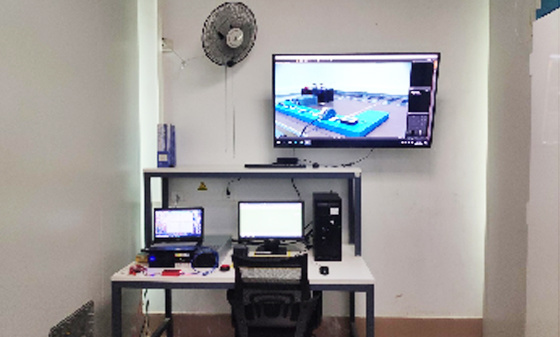 EMS test - low-frequency magnetic field anti-interference test
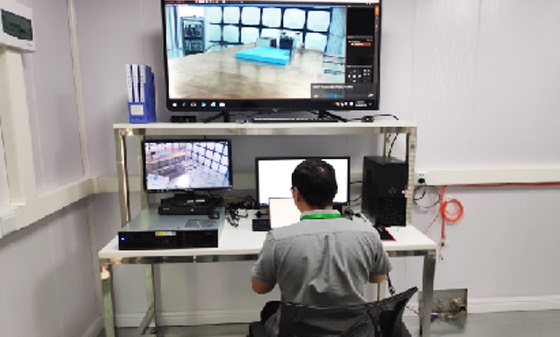 EMI Testing - Transient Conducted Emissions Testing System
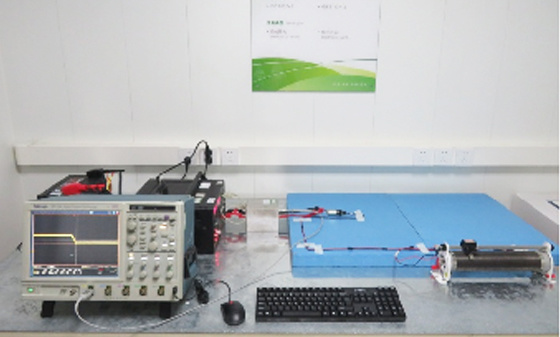 EMI testing - low-frequency magnetic field emission
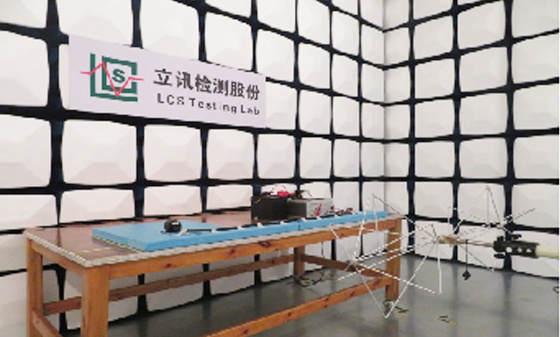 EMI Test - Radiation Emission Test
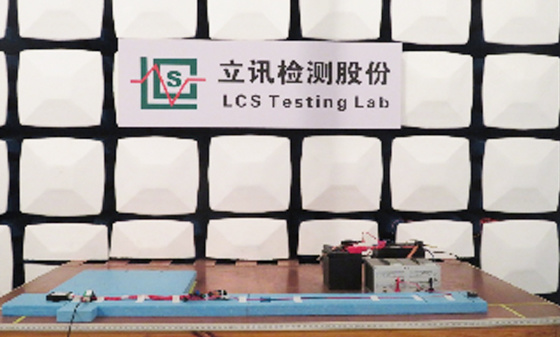 EMI Test - Conducted Emissions Test
 Automotive Electronic Testing
Automotive Parts Inspection
 Automotive ELV&VOC
 Reliability testing
 Temperature shock test
 Vibration testing
 Instrument panel/instrument panel three comprehensive vibration test
 Comprehensive vibration test of door inner panel III
 Sunvisor Three Comprehensive Vibration Test
 Spoiler Three Comprehensive Vibration Test
 Three comprehensive vibration tests of car front and rear bumpers
 Three comprehensive vibration tests for lamp housing/lampshade
 Comprehensive vibration test of outer circumference three
 Automotive metal material testing
 Performance testing of automotive lighting fixtures
 Rapid temperature change test
 Vibration
 Common issues with vibration testing
 Common issues with fatigue testing
 Common issues with high and low temperature testing
 Conducted Interference (CE) - Suzhou Lixun Standard
 Electromagnetic Radiation Tolerance Test (RS) - Suzhou LCS Standard
 Electrical Fast Pulse Withstand Test (EFT) - Suzhou LCS Standard
 Voltage flicker test - Suzhou LCS standard
Electronic appliances
 Household appliance product testing
 Electrical accessory product testing
 Household appliance testing
Chemical Testing
 Introduction to PFAS Testing
 MOSH/MOAH Mineral Oil Testing Service
 MOSH/MOAH Mineral Oil Testing and Certification Report Service
 Consumer Product Testing Services - WEEE Chapter
 Ecological textile testing
 Leather Footwear Inspection
 Food contact material testing
 Testing of toys and baby products
 Hazardous substance testing
Electronic Cigarette Testing
 Electronic cigarette detection
Reliability testing
 Other tests - pencil hardness test
 Mechanical testing - Packaging compression test
 Climate environment testing - Xenon lamp aging test
Battery Testing
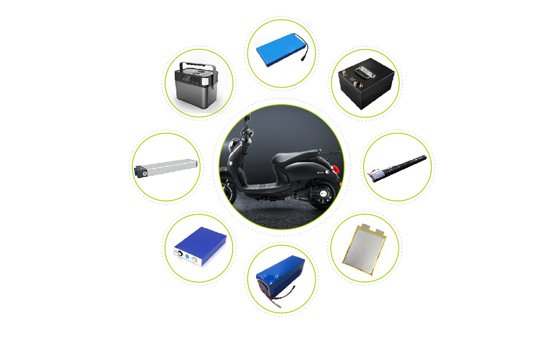 Power storage battery testing and certification
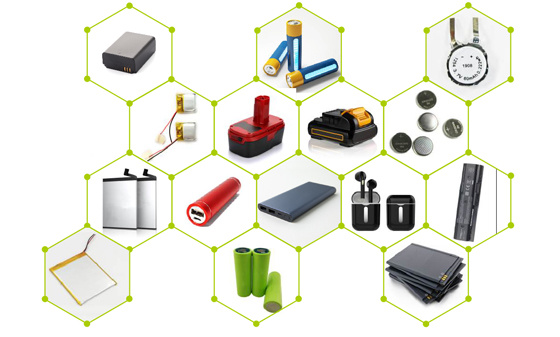 Consumer Electronics Battery Testing and Certification
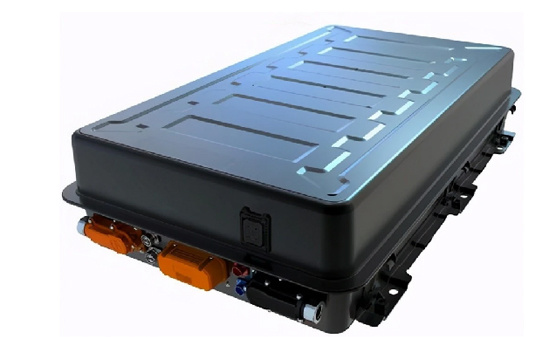 power battery
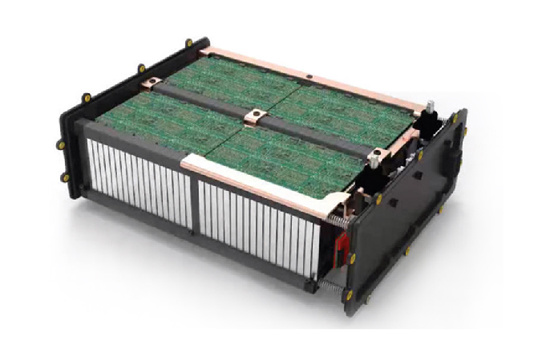 Light electric vehicle batteries
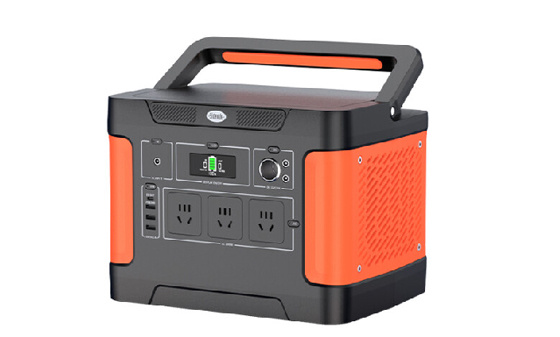 Energy storage battery
 Portable battery
 Battery testing
 battery test
Lamp Inspection
 Inspection of ship lighting fixtures
 COI Index Test for Medical Indoor Lighting
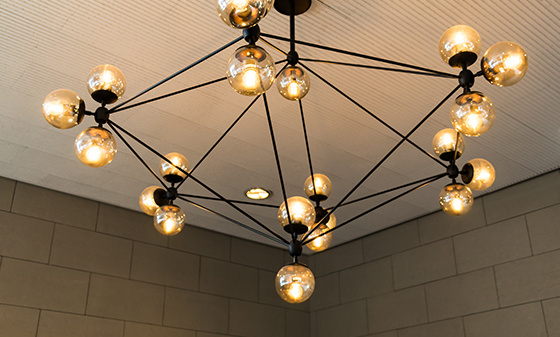 Lamp safety inspection
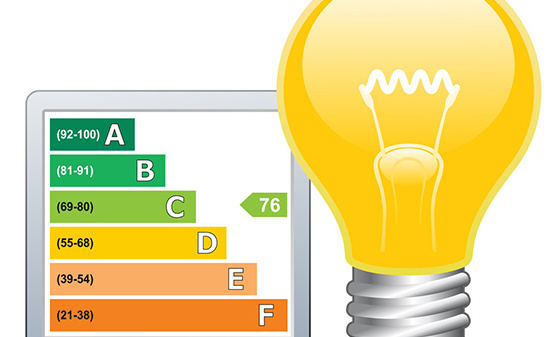 Luminaire energy efficiency testing
 EMC testing of lighting fixtures
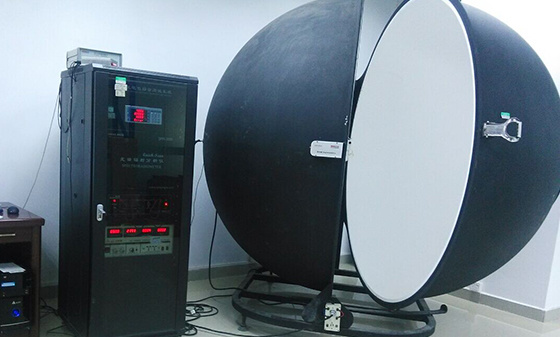 Integral Ball Laboratory
 Photobiology Experiment
 Light distribution test
 Lamp aging test
 Lamp IP waterproof
 Lamp performance testing
 Lamp reliability testing
Children's toy testing
 Testing standards for toy products
China Certification
 China's "national promotion" RoHS certification
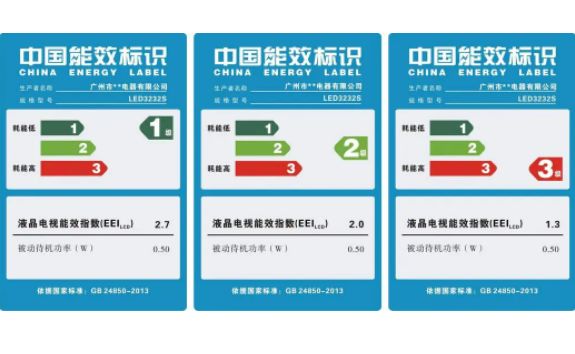 China Energy Efficiency Label Certification
 China Energy Conservation Certification
 China CQC Certification
 Tmall JD Quality Inspection Report
 China SRRC Certification
 Taiwan BSMI certification
 Taiwan NCC certification
 China CCC Compulsory Certification
Asia Certification
 Vietnam certification
 KC certification
 KUCAS Certification in Kuwait
 Singapore PSB certification
 Iraq COC Certification
 IMDA certification
 VCCI Certification in Japan
 JATE certification in Japan
 PSE certification
 BIS certification
 Japanese TELEC certification
European Certification
 RoHS certification
 GOST certification in Russia
 Russian EAC certification
 Northern Ireland UKNI logo
 Electrical ENEC certification
 European D-MARK certification
 Türkiye BTK certification
 TSE certification in Türkiye
 CE certification in Türkiye
 RED certification
 German TUV-SUD certification
 CE-ERP certification
 REACH certification
 German GS certification
 EU E-Mark certification
North American Certification
 Ecuador VOC certification
 Mexico NOM certification
 IRAM certification
 CPSC Certification in the United States
 CSA certification
 ASTM certification
 FDA certification
 CEC certification
 ETL certification
 ul certification
 IC certification
 Energy Star
 FCC Certification in the United States
 ASTM certification
Middle East Certification
 Israel SII certification
 Saudi SABER certification
 GCC certification for the seven Gulf countries
 Iran COI certification
 Qatar COC Certification
 Iraq COC Certification
 Saudi EER Energy Efficiency Certification
 Saudi SABER certification
 Algeria PCA certification
 PVOC certification
Australia Certification
 New Zealand IC-F testing
 VEET certification
 LCP certification
 GEMS certification
 RCM certification
 C-Tick certification
 SAA certification
Africa Certification
 Gabon COC certification
 Algeria COC certification

 Ethiopian VOC and COC certification
 Mauritius VOC certification
 Ghana COC certification
 COC certification in Burundi
 Zambia COC certification
 Botswana COC Certification
 Uganda PVOC certification
 SABS certification in South Africa
 South African LOA certification
 Zimbabwe CBCA Certification
 Nigeria SONCAP certification
 Kenya PVOC certification
 African COC certification
Other certifications
 WEEE
 Bluetooth BQB certification
 IECEE registration
 MHRA registration in the UK
TRAINING
 Management system training
 Laboratory technical training
 Laboratory Process Consulting
 Laboratory decoration construction
Wireless Communication
Electromagnetic compatibility
Automotive Electronics
Automotive Parts Inspection
Electronic appliances
Chemical Testing
Electronic Cigarette Testing
Reliability testing
Battery Testing
Lamp Inspection
Children's toy testing
China Certification
Asia Certification
European Certification
North American Certification
Middle East Certification
Australia Certification
Africa Certification
Other certifications
TRAINING
Wireless Communication
Electromagnetic compatibility
Automotive Electronics
Automotive Parts Inspection
Electronic appliances
Chemical Testing
Electronic Cigarette Testing
Reliability testing
Battery Testing
Lamp Inspection
Children's toy testing
China Certification
Asia Certification
European Certification
North American Certification
Middle East Certification
Australia Certification
Africa Certification
Other certifications
TRAINING
Wireless Communication
Electromagnetic compatibility
Automotive Electronics
Automotive Parts Inspection
Electronic appliances
Chemical Testing
Electronic Cigarette Testing
Reliability testing
Battery Testing
Lamp Inspection
Children's toy testing
China Certification
Asia Certification
European Certification
North American Certification
Middle East Certification
Australia Certification
Africa Certification
Other certifications
TRAINING
Wireless Communication
Electromagnetic compatibility
Automotive Electronics
Automotive Parts Inspection
Electronic appliances
Chemical Testing
Electronic Cigarette Testing
Reliability testing
Battery Testing
Lamp Inspection
Children's toy testing
China Certification
Asia Certification
European Certification
North American Certification
Middle East Certification
Australia Certification
Africa Certification
Other certifications
TRAINING
Wireless Communication
Electromagnetic compatibility
Automotive Electronics
Automotive Parts Inspection
Electronic appliances
Chemical Testing
Electronic Cigarette Testing
Reliability testing
Battery Testing
Lamp Inspection
Children's toy testing
China Certification
Asia Certification
European Certification
North American Certification
Middle East Certification
Australia Certification
Africa Certification
Other certifications
TRAINING
Wireless Communication
Electromagnetic compatibility
Automotive Electronics
Automotive Parts Inspection
Electronic appliances
Chemical Testing
Electronic Cigarette Testing
Reliability testing
Battery Testing
Lamp Inspection
Children's toy testing
China Certification
Asia Certification
European Certification
North American Certification
Middle East Certification
Australia Certification
Africa Certification
Other certifications
TRAINING

Interpretation of EU CRA New Regulations: How Enterprises Can Build a Future oriented Vulnerability Governance System
Author.
LCS
Source:
Post time:
2026-03-20
In November 2024, the EU's "Network Resilience Act" was officially implemented. For all product manufacturers containing digital elements, this is not only a new regulation, but also a fundamental change in the product security governance model. Among them, a systematic and sustainable vulnerability management and disclosure mechanism has become an essential key to unlocking the EU market.

This article will provide you with a clear breakdown of CRA's core obligations and indicate the practical path from existing foundations to compliance.
Core obligation: Accurately understand "must report" and "not report"
The core of CRA is to require reporting of vulnerabilities and serious security incidents that have been actively exploited. The key lies in accurate judgment, avoiding resource waste or false alarms.
⏰ Scenarios that must be reported
When a vulnerability meets the criteria of 'exploited' and 'severely impacted', the following timeline must be strictly followed:
Within 24 hours: Submit early warning.
Within 72 hours: Submit detailed notification.
Within one month: submit a complete technical analysis report.
The report needs to be submitted through both the EU unified platform (ENISA operation) and the CSIRT channels of member states.
✅ Scenario without mandatory reporting
The following situations are usually not within the mandatory scope (unless they are actually utilized later):
Vulnerabilities that are only discovered through scanning but cannot be actually exploited.
Common or business logic vulnerabilities received in the vulnerability reward program.
A loophole that is still in the research stage and has not been exploited.
At the same time, CRA requires companies to establish an open and transparent mechanism for coordinating vulnerability disclosure, including public reporting channels, clear time commitments, and a positive communication mechanism with security researchers. This means that establishing a dedicated organizational capability similar to PSIRT (Product Safety Incident Response Team) is no longer an option, but a mandatory regulation.
Fundamental transformation: from "delivery endpoint" to "service endpoint"
CRA has completely changed the safety responsibility cycle of products. The sale of a product is not the end point, but the starting point for manufacturers to provide continuous safety services.
According to regulations, during the entire product support period (generally not less than 5 years), manufacturers must:
Continuously monitor vulnerability intelligence.
Regularly conduct safety assessments.
Provide timely security verified patches and updates.
This requires enterprises to have mature OTA or patch distribution capabilities and internalize security maintenance as a long-term service.
Turning Challenges into Opportunities: Building Sustainable Vulnerability Management Processes
Faced with CRA requirements, enterprises often face three major challenges: unclear organizational responsibilities, weak SBOM and patch management in technology, and difficulty in proving compliance. The process of overcoming these challenges is precisely the process of building the core security capabilities of the enterprise.

Enterprises need to establish a closed-loop vulnerability management process that covers:
Entrance: Establish clear channels for receiving vulnerabilities.
Handling: Implement vulnerability recording, grading, analysis, and impact assessment.
Fix: Develop strategies, develop and validate patches.
Closed loop: Safely release updates and complete notifications and archiving.
Related articles
New articles
Media Center
Latest News
Contact Us
National 24-hour service hotline
400-116-2629
Group Headquarters
E-mail: webmaster@lcs-cert.com
Address: Shenzhen City, Baoan District, Shajing Street, Nga side of the school of Wei Juji Industrial Park, Building A 1 ~ 2 floor, Building C 3 floor


 WeChat Inquiry


 Reservation


Contact Us
National 24-hour service hotline
Address:Juji Industrial Park, Xueziwei, Ngabian, Shajing Street, Baoan District, Shenzhen Building A 1~2F, Building C 3F

WeChat public number
Share industry dry goods

WeChat consultation
Please note consulting services

Follow Jitterbug

Mobile website
di complaint mailbox: customer.complaint@lcs-cert.com complaint telephone tel: 18126445450 certificate report verification of authenticity mailbox: verification@lcs-cert.com